What Should Standards Compliance Analysis Training Cover Before an Audit?
Author
Date Published
Reading Time
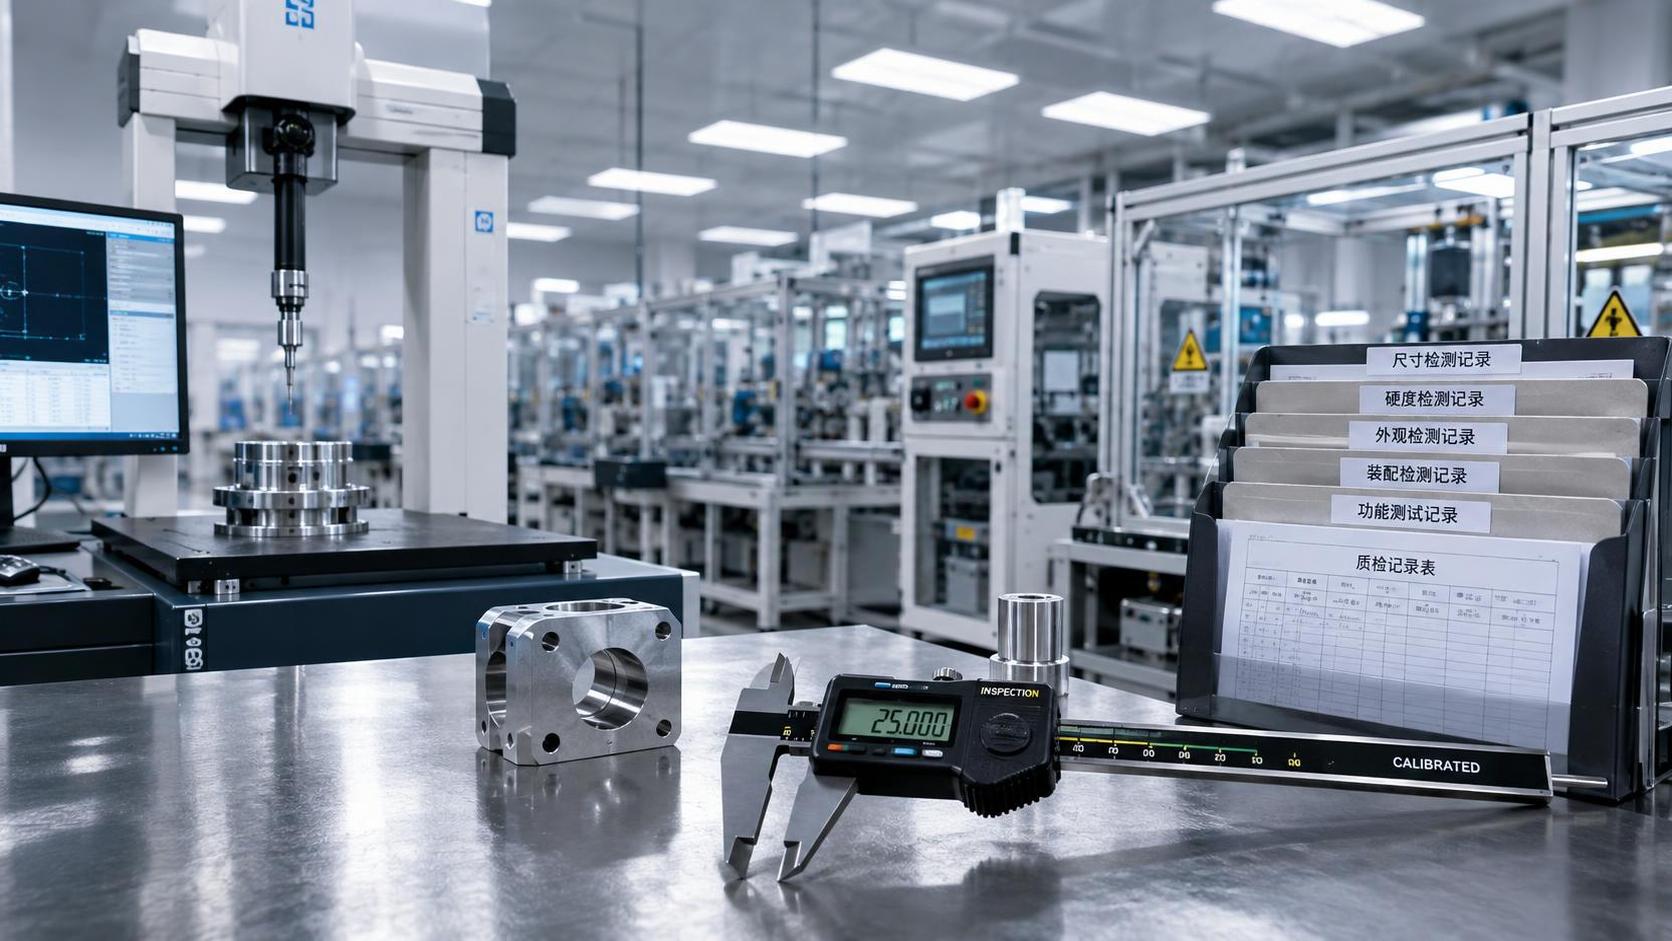
An audit rarely fails because a team has never heard of ISO, CE marking, UL requirements, or internal procedures. It fails because people cannot connect those requirements to the equipment on the floor, the records in the system, and the decisions made during normal work. A missing calibration label may be obvious. A measurement result traced to an expired reference standard, an undocumented engineering change, or a risk control that was never verified is harder to spot—and far more likely to trigger serious questions.
That is why standards compliance analysis training should begin well before the auditor arrives. For quality and safety leaders in industrial operations, the practical goal is not to memorize clauses. It is to build a team that can determine which requirements apply, test whether controls are actually working, locate defensible evidence, and explain gaps without improvising.
Start With Scope, Not With a Generic Checklist
The first training topic should be audit scope. This sounds basic, but it is where many internal reviews lose discipline. Teams often apply a broad corporate checklist to a narrow manufacturing line, a field installation, or a new product release. The result is wasted effort in some areas and blind spots in others.
Training should teach personnel to define the boundaries of the audit in operational terms: sites, production cells, outsourced processes, product families, software revisions, markets of destination, and relevant time periods. A facility may operate under an ISO management system while also placing electrical assemblies into markets that require product-specific conformity assessment. Those are connected issues, but they are not the same thing.
For example, CE marking is not a blanket “European certificate” for every industrial product. Its application depends on the applicable EU legislation, the product category, the manufacturer’s conformity assessment route, technical documentation, declarations, and any involvement required from a notified body. Likewise, UL may refer to product testing, listing, recognition, or other evaluation pathways; the precise expectation depends on the product, use case, and authority having jurisdiction. Training that treats these terms as interchangeable badges creates risk before any audit begins.
A useful exercise is to have cross-functional participants build an applicability matrix. It should link each product or process to the governing standard, regulatory or contractual requirement, edition or revision where relevant, responsible owner, objective evidence, and any open interpretation issue. If the team cannot explain why a requirement applies—or does not apply—the matrix is not ready.
Teach People How to Read a Standard Against the Real Process
The core of standards compliance analysis training is interpretation. Auditors do not usually expect every operator to quote a clause verbatim. They do expect process owners to understand the intent behind the requirement and demonstrate how their operation meets it.
Training should therefore move beyond slide-based overviews. Use a live work instruction, inspection plan, lockout procedure, welding record, calibration certificate, or environmental monitoring log. Ask participants to identify the relevant requirement, the operational control, the evidence that proves it happened, and the consequence if the control fails. This is where vague phrases such as “we follow the procedure” become testable.
In heavy industry, the evidence chain often crosses departments. Procurement may qualify a supplier; engineering may approve a material substitution; quality may inspect incoming goods; production may assemble the item; and maintenance may preserve the equipment used to verify it. Training should make those handoffs visible. A compliant purchase order alone does not prove that the delivered item matched the specified grade, rating, traceability requirement, or revision-controlled drawing.
This matters especially in sectors involving power distribution, safety equipment, instrumentation, environmental controls, and structural or metallurgical components. The more severe the operating conditions, the less defensible it is to rely on assumptions. A certificate of conformity may support a claim, but it does not replace incoming verification where the contract, risk level, or applicable procedure requires it.
Build a Requirement-to-Evidence Map Before Reviewing Documents
Many organizations prepare for an audit by collecting records in a rush. That can produce a large folder and a weak audit position. The better approach is to identify the evidence path for each significant requirement before anyone starts searching for files.
A requirement-to-evidence map is one of the most practical tools to cover in training. It forces the team to distinguish between a document that describes intended control and a record that proves control occurred. A procedure may state that gauges are calibrated. The supporting evidence may include an equipment register, calibration status, certificates, out-of-tolerance assessments, and records showing that affected measurements were evaluated when a problem was discovered.
This mapping exercise also exposes “evidence islands”: records held by one function that nobody else can retrieve or interpret. A safety manager may know where training records are stored, while a maintenance supervisor holds inspection logs locally and engineering controls the latest drawings in a separate platform. That is manageable only if ownership and retrieval routes are clear before the audit.
Include Risk-Based Thinking, but Keep It Specific
Risk-based thinking has become familiar language, yet training often leaves it at the level of a generic risk register. Before an audit, teams need to connect risk to controls and then to proof. If a pressure, electrical, guarding, chemical exposure, or measurement error could create a significant safety or quality consequence, the training should ask a direct question: what prevents the event, how is that prevention checked, and what happens when the check fails?
For safety-related controls, participants should understand the distinction between a risk assessment completed during design and the ongoing verification of safeguards in operation. A machine guard can be specified correctly and still become ineffective after maintenance, unauthorized modification, or poor restart discipline. Similarly, a lockout/tagout procedure is not validated merely because a current document exists. Competence, field practice, isolation points, periodic inspection, and incident learning all matter.
Environmental and utility systems need the same attention. Where a site controls emissions, wastewater, hazardous materials, energy isolation, or spill response, the applicable legal and permit conditions must be checked against local requirements rather than assumed from an international standard. Training should clearly flag where specialist legal or technical review is needed. Internal auditors should not be encouraged to make regulatory interpretations beyond their competence.
Train for Traceability Through the Entire Chain
Auditors frequently test traceability by starting with one sample and moving in the least convenient direction. They may select a finished assembly and ask for incoming material records, test reports, inspection data, operator qualifications, and shipment release. Or they may take a supplier certificate and ask which batches, serial numbers, or installed assets it actually supports.
Good training uses this “follow the trail” method. Select a real but controlled sample and reconstruct its history. Can the team link the item to the correct specification revision? Can it show who inspected it, with what instrument, under what acceptance criteria? If a component was reworked, was the rework authorized and reinspected? If there was a supplier deviation, was its impact evaluated before use?
For instruments and measurement systems, this should include metrological traceability where required by the organization’s system or the applicable standard. The point is not that every instrument needs the same level of control. A tape measure used for rough layout does not present the same risk as a device used to accept a critical tolerance. Training should help teams justify the level of control from the intended measurement and its effect on conformity.
Make Corrective Action More Than a Better Explanation
An audit finding is not resolved because the team has written a polished response. Standards compliance analysis training should cover containment, root-cause analysis, correction, corrective action, effectiveness review, and closure criteria. These terms are often blurred in practice.
Containment protects the immediate situation. Correction fixes a known issue. Corrective action addresses the cause of recurrence. If an inspection record is incomplete, filling in a missed field may be a correction. It does not explain why the field was missed, whether similar records are affected, or whether the form, training, workflow, supervision, or system design allowed the error to recur.
Teams should be trained to avoid two common weaknesses. One is blaming “operator error” without examining the system around the operator. The other is jumping to a large procedural rewrite when a targeted control would be more effective. A useful corrective action has a clear owner, due date, verification method, and evidence of effectiveness. It should also be proportionate. Not every clerical mistake needs a site-wide overhaul; repeat failures in a critical safety control should never be treated as paperwork.
Practice the Audit Conversation, Not Just the Internal Review
Auditor interviews can reveal a disconnect that document reviews miss. A supervisor may describe a process differently from the documented instruction. An operator may be using a local workaround that quality has never seen. A maintenance technician may know that a safety interlock is unreliable but assume that production management already accepted the risk.
Mock interviews are valuable when they are realistic and non-punitive. Train people to answer from their own responsibility, show the actual record when asked, and avoid guessing. “I need to verify that with the process owner” is a better response than an unsupported claim. At the same time, quality and safety leaders should understand that coaching people to hide uncertainty is not audit preparation. It is a way of delaying a problem until it becomes more expensive.
The strongest mock audits include a floor walk, a document sample, an interview, and a traceability challenge. They should also test practical details: are emergency procedures accessible, are controlled documents current at the workstation, are inspection criteria readable, and can staff identify what to do with nonconforming material? Small inconsistencies are often the clues that lead an auditor to a wider process question.
Use Technical Intelligence Carefully Across Global Operations
For EPC contractors, facility managers, and industrial procurement teams, compliance analysis is increasingly shaped by global supply chains. Product claims, test documentation, material declarations, and installation conditions may originate in different jurisdictions. A training program should therefore include supplier-document review, specification flow-down, authenticity checks where appropriate, and escalation routes for conflicting requirements.
This is also where technical intelligence platforms such as Global Industrial Core can be useful: not as a substitute for the applicable standard, the manufacturer’s technical file, or qualified legal advice, but as a structured source for comparing safety, measurement, power, environmental, and mechanical considerations across industrial projects. The final compliance decision still belongs to the responsible organization and must be grounded in the actual product, installation, market, and contractual scope.
Before the audit, the most useful question is not “Do we have all the documents?” It is “Can we demonstrate that our stated controls are understood, performed, monitored, and improved when they fail?” If the answer is clear for the highest-risk processes, the audit becomes a verification of disciplined work rather than a scramble to defend a filing system.
Technical Specifications
- How to Select Electronic Hotel Key Card Locks for Guest Rooms and Staff AreasAuthor :Safety Compliance Lead
- How to Select Lab Instruments for Reliable Chemical Analysis WorkflowsAuthor :Precision Metrology Expert
- How to Size a UPS for Server Rooms: Load, Runtime, and Redundancy FactorsAuthor :Grid Infrastructure Analyst
Expert Insights

Chief Security Architect
Dr. Thorne specializes in the intersection of structural engineering and digital resilience. He has advised three G7 governments on industrial infrastructure security.
Related Analysis
- Sep 17, 2026How to Select Electronic Hotel Key Card Locks for Guest Rooms and Staff AreasAuthor :Safety Compliance Lead
- Sep 16, 2026How to Select Lab Instruments for Reliable Chemical Analysis WorkflowsAuthor :Precision Metrology Expert
- Sep 15, 2026How to Size a UPS for Server Rooms: Load, Runtime, and Redundancy FactorsAuthor :Grid Infrastructure Analyst
Core Sector // 01
Security & Safety
- What to Check When Sourcing Vibration Meters Wholesale for Industrial MaintenanceAuthor :Precision Metrology Expert

- How to Select Process Control Instruments for Accuracy, Safety, and UptimeAuthor :Precision Metrology Expert

- What Should Standards Compliance Analysis Training Cover Before an Audit?Author :Precision Metrology Expert

- Why Do Pressure Instruments Fail in High-Vibration Sites?Author :Precision Metrology Expert

- Is FM Software Integration Needed for Overseas Instrument Maintenance?Author :Precision Metrology Expert

- What Are the Differences Between Lab and Field Testing Equipment?Author :Precision Metrology Expert

- Is Independent Testing Necessary for Critical Safety Components?Author :Precision Metrology Expert

- How to Validate Industrial Application Scenarios Before ProcurementAuthor :Precision Metrology Expert