Is Independent Testing Necessary for Critical Safety Components?
Author
Date Published
Reading Time
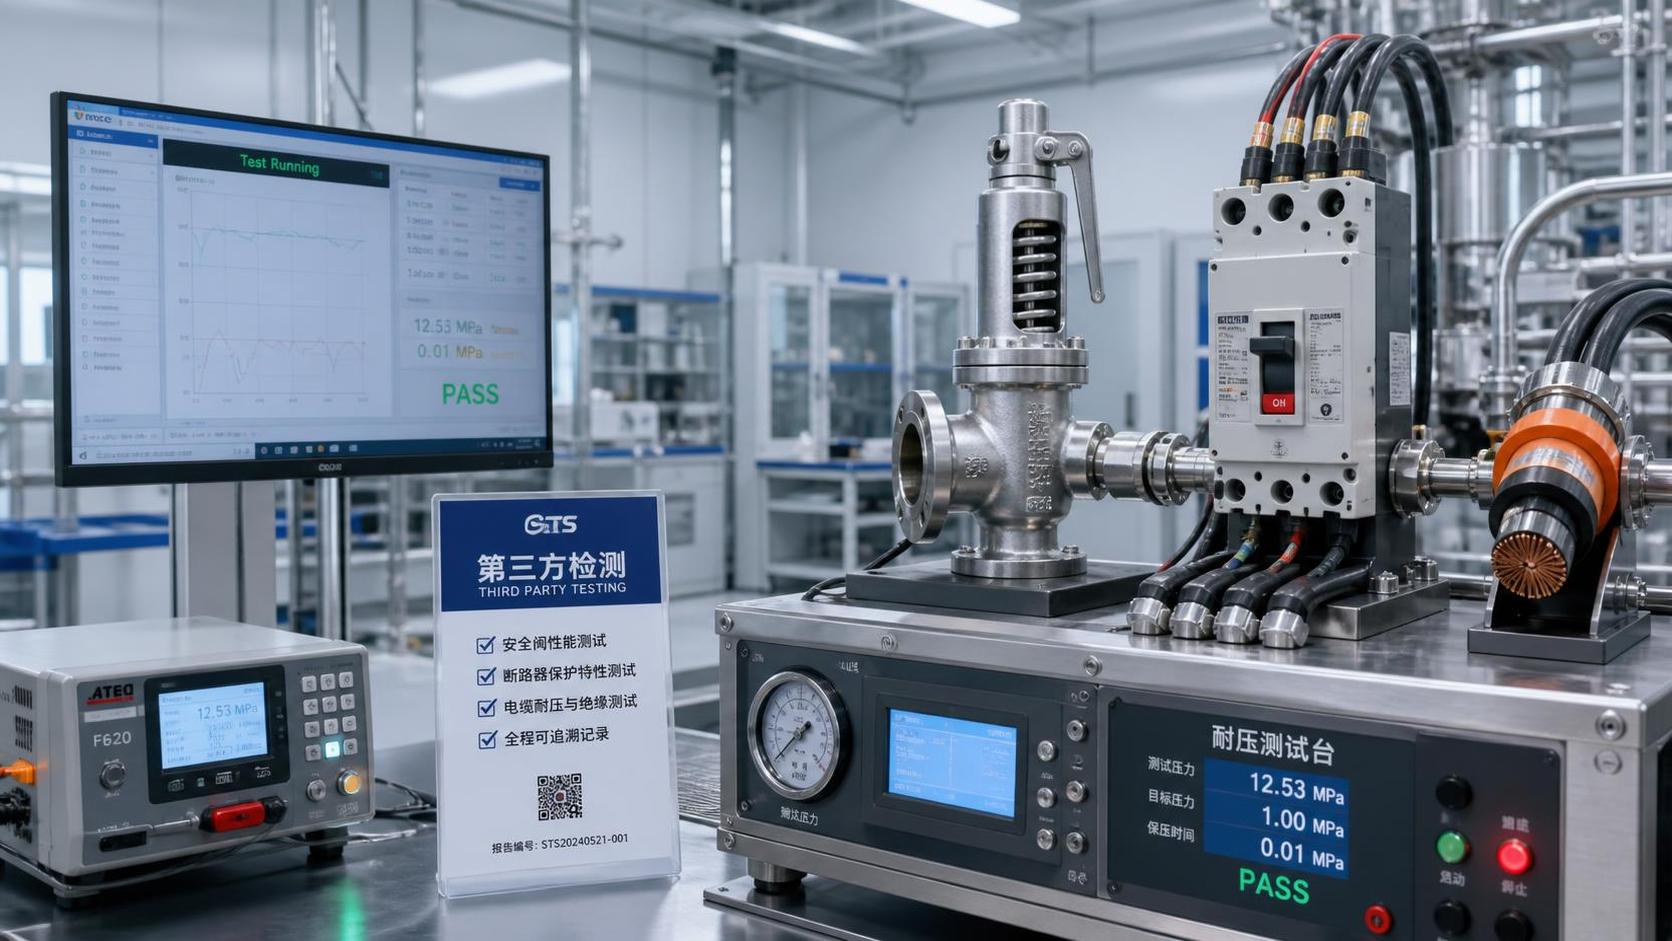
The short answer to is it necessary to get independent testing for critical infrastructure safety components is: often yes, but not in every procurement situation and not in the same form. Where a component prevents fire, electrical shock, pressure release, structural failure, toxic exposure, or loss of a safety function, an independent test report can be the difference between documented confidence and an unsupported supplier claim.
The harder question is not whether third-party testing sounds desirable. It is whether the testing is relevant to the actual component, installation, operating environment, and regulatory obligation. A laboratory report for a standard indoor condition may offer limited reassurance for equipment that will face salt spray, vibration, dust, extreme heat, or repeated emergency operation.
For critical safety components, independent verification is best treated as a risk-control decision. It should be proportional to the consequence of failure, the maturity of the supplier, the complexity of the component, and the ability to inspect performance after installation.
Is It Necessary to Get Independent Testing for Critical Infrastructure Safety Components?
Independent testing is generally necessary when failure could create a serious safety event, interrupt an essential service, trigger a legal or contractual breach, or remain hidden until an emergency occurs. It is especially relevant when the buyer cannot reasonably confirm the claimed performance through incoming inspection, routine commissioning, or normal maintenance.
Examples include fire-rated barriers and doors, emergency shutdown devices, pressure-relief equipment, electrical protection devices, gas detection systems, safety interlocks, fall-protection anchors, cable assemblies used in life-safety circuits, and components installed in hazardous or harsh environments. In these cases, material appearance and a supplier declaration alone do not prove that the item will perform as required.
That does not mean every bolt, bracket, enclosure, or replacement part must be sent to an outside laboratory before purchase. A low-consequence, well-specified component sourced from a qualified manufacturer may be controlled through certificates of conformity, traceable material records, factory quality documentation, and receiving inspection. The line changes when a defect cannot be detected easily, the part is safety-critical, or the stated rating is central to the design basis.
A practical rule: seek independent evidence when you would be unable to defend the component choice after an incident by relying only on the manufacturer’s own statement. The evidence should address the performance claim that matters most, rather than merely showing that the product passed an unrelated test.
Manufacturer Testing and Independent Testing Are Not the Same Thing
Both forms of testing have a place. The mistake is assuming that one automatically replaces the other.
A capable manufacturer may operate a robust internal laboratory, follow documented procedures, and maintain strong traceability. That is valuable evidence, particularly for repeat orders and established products. Yet independence adds credibility because the party verifying the claim does not have a direct commercial interest in the sale of the item.
There is also a practical distinction between a test report and a certification. A report usually records the outcome of testing on a particular sample under defined conditions. Certification may involve a broader process that can include product evaluation, factory surveillance, quality-system review, and rules for ongoing use of a certification mark. Buyers should not assume these documents mean the same thing.
When Third-Party Verification Becomes Essential
Some triggers should move independent testing from “nice to have” to a procurement requirement.
- The specification or contract requires it. Public works, major industrial projects, insurers, owners, and engineering specifications may name an accepted standard, approval route, or accredited testing requirement. In that case, a supplier brochure is not an equivalent substitute.
- The component carries a life-safety function. If it must operate correctly during a fire, power fault, overpressure event, evacuation, or containment failure, independent evidence is normally justified.
- The claimed performance cannot be checked on site. Fire resistance, arc-fault behavior, long-term corrosion resistance, ingress protection, and fatigue performance are not confirmed by a visual inspection at delivery.
- The supply chain has changed. A new factory, substitute material, revised design, unfamiliar distributor, or cross-border source can invalidate assumptions built around an earlier approval.
- The operating condition is unusual. Offshore exposure, seismic loading, explosive atmospheres, high humidity, extreme temperatures, chemical contact, or constant vibration may require evidence beyond a standard catalog rating.
- The failure consequence is disproportionate to the part cost. A relatively inexpensive sensor, seal, connector, or actuator can disable a much larger safety system. Unit price is a poor proxy for criticality.
One recurring problem is treating a component as non-critical because it is small. In reality, many incidents begin at interfaces: an incompatible cable gland, an incorrectly rated fuse, a seal that degrades in process chemicals, or a valve accessory that prevents a shutdown valve from reaching its safe position. The relevant question is what the part can cause the system to do, or fail to do.
Standards Matter Only When They Match the Real Requirement
Buyers often ask for “CE, UL, or ISO certification” as a general safeguard. That language is understandable, but it can conceal a gap in the requirement. CE marking is generally a manufacturer declaration that a product meets applicable European Union requirements; it is not, by itself, proof that every product has been independently tested. UL may refer to testing, listing, recognition, or other services depending on the product and market. ISO standards cover many subjects, and an ISO 9001 certificate for a manufacturer’s quality management system does not prove the performance of a particular safety component.
The useful starting point is the functional claim. What must the component withstand, detect, contain, isolate, or control? Then identify the applicable jurisdiction, project specification, installation code, and recognized test method. The exact standard and approval route should be confirmed against current official requirements and the authority having jurisdiction where relevant.
For example, an enclosure may need an ingress-protection rating, but that does not establish suitability for a corrosive atmosphere. A fire-stopping product may have a test result, but the tested wall type, penetration arrangement, service material, gap size, and installation orientation may differ from the planned installation. An electrical device may be listed for one voltage, wiring method, or enclosure arrangement but not another.
This is why a document review should go beyond checking a logo or certificate number. Compare the evidence to the exact purchase specification and installation details. A legitimate report can still be irrelevant to the use case.
What to Review Before Accepting a Test Report
A reliable document review does not need to become a legal audit, but it does need more care than confirming that a PDF exists. Start with the product identity: manufacturer, model, revision, materials, dimensions, and relevant accessories. If the report refers to a family of products, determine whether the supplied configuration is actually covered.
Then examine the test scope. Look for the standard or method used, test conditions, pass criteria, sample preparation, limitations, report issue date, and whether modifications since testing are disclosed. A report for a prototype deserves different scrutiny from a current production product with traceable manufacturing controls.
Accreditation can also matter. Laboratories may hold accreditation to ISO/IEC 17025 for defined testing activities, but accreditation is scope-specific. It is reasonable to verify that the laboratory’s accredited scope covered the relevant test at the time it was performed. Similarly, a certification body’s status should be checked through the appropriate official directory or the issuing organization, not solely through a supplier-provided image.
Ask one uncomfortable but useful question: “What would make this report inapplicable?” Suppliers with mature compliance systems can usually answer clearly. Warning signs include missing page numbers, altered scans, inconsistent model names, expired approvals presented as current, certificates belonging to a different legal manufacturer, and vague statements such as “tested to international standards” without naming the standard or test result.
Testing the Product Is Not Enough if Installation Can Defeat It
Independent product testing addresses a defined sample under defined conditions. Infrastructure performance also depends on storage, installation, commissioning, maintenance, and system integration. This is particularly important for passive fire protection, protective relays, emergency power equipment, pressure systems, detection systems, and mechanical safety assemblies.
A properly tested fire-rated penetration seal can fail if installers use unapproved backing material or change the cable arrangement. A listed electrical protective device can be unsuitable if fault-current capacity, coordination, or enclosure heat dissipation is overlooked. A gas detector can have valid performance evidence yet provide poor protection if sensor placement, calibration intervals, alarm logic, and ventilation assumptions are wrong.
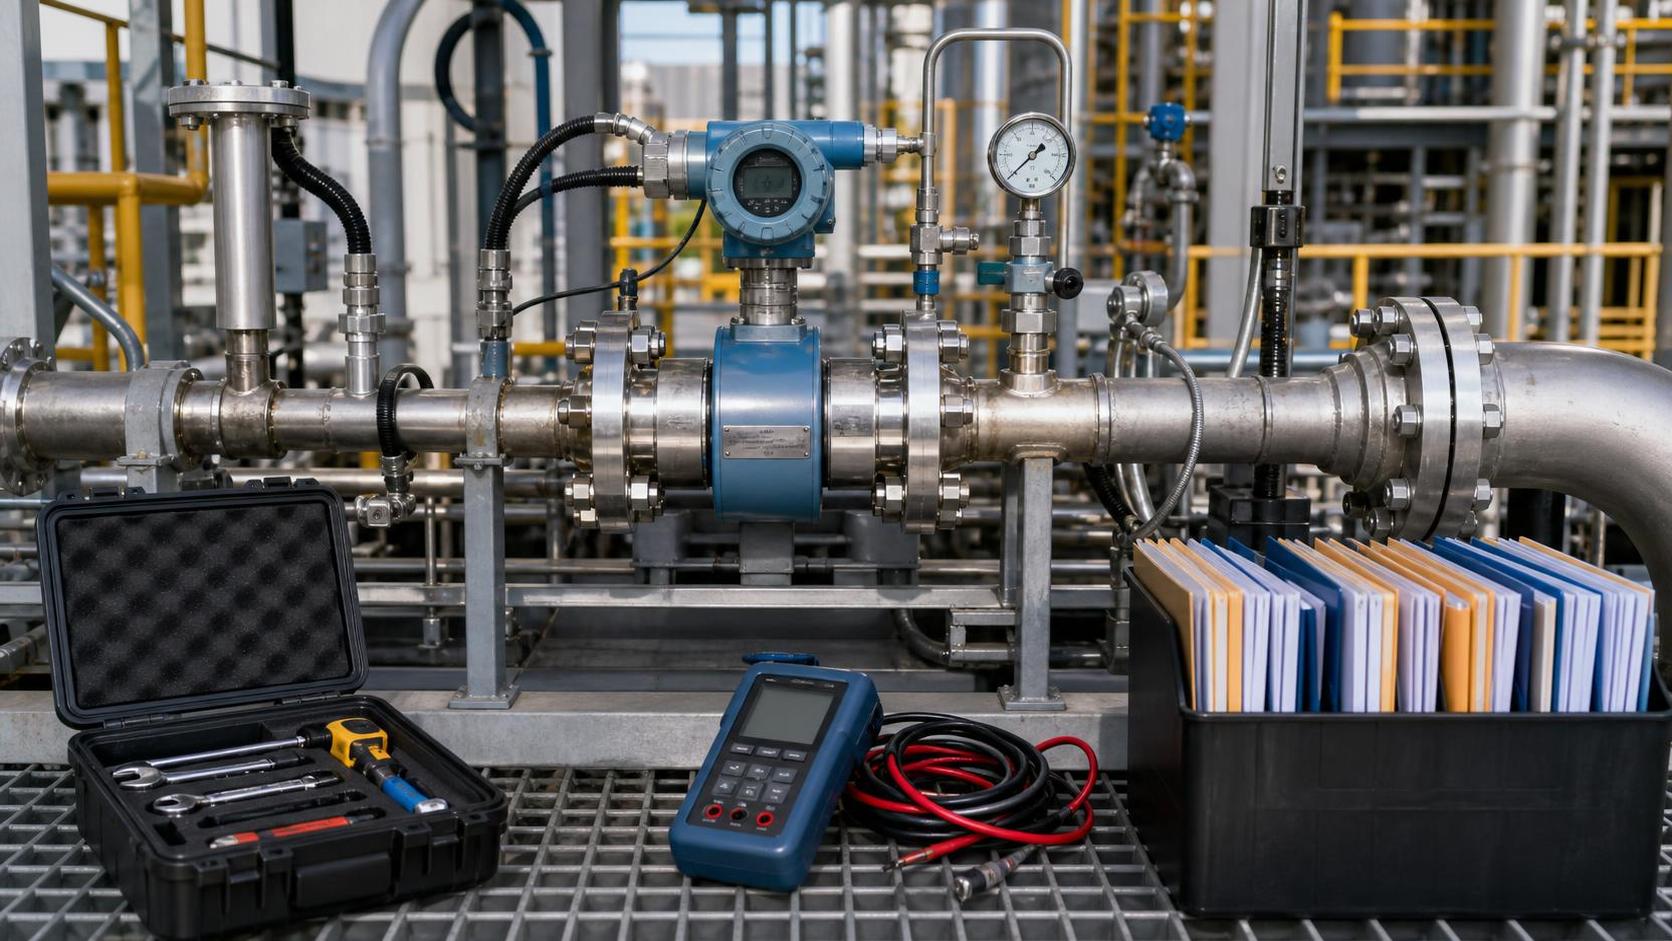
For higher-risk work, use a layered evidence package: independent type-test evidence, production quality records, lot or serial traceability, installation instructions, competent installation, commissioning records, and periodic inspection. Each layer catches a different category of failure. No single certificate carries the full burden.
How to Decide Without Turning Every Purchase Into a Laboratory Project
The most efficient approach is to classify components before sourcing begins. Define which items are safety-critical, which are important but replaceable, and which are routine. For critical items, state the required evidence in the technical specification and procurement schedule. That avoids the common late-stage argument in which a supplier offers documents that were never clearly requested.
For a first-time supplier or an unfamiliar product, request documents early enough for engineering review. Do not wait until goods are at the gate. If the component is modified, verify whether the modification affects the approval or test coverage. Changes in material grade, wall thickness, software version, connector type, coating, sealing compound, or manufacturing location can matter far more than they appear to in a commercial submittal.
Independent testing may be unnecessary for a low-risk standard item where the supplier is qualified, the intended use is conventional, requirements are clear, and incoming checks can confirm the necessary attributes. It is also not a cure for poor engineering. Testing cannot validate an incomplete design basis or make an incorrectly selected component suitable for service.
Global Industrial Core approaches this issue as an evidence-chain problem rather than a paperwork exercise. Safety, measurement, electrical, environmental, and mechanical decisions need documentation that connects the component to its claimed duty. For buyers comparing technical submissions, the strongest choice is usually the one whose performance evidence, traceability, and installation limits can be understood and verified without relying on ambiguous marketing language.
Frequently Asked Questions
Is a supplier declaration of conformity enough for a safety component?
It can be enough only when the applicable rules allow it and the risk is appropriately controlled. For life-safety functions, regulated applications, or unfamiliar sources, independent evidence is usually more defensible.
Does a CE mark prove independent laboratory testing?
No. CE marking and third-party testing are not interchangeable. The required conformity assessment route depends on the product and applicable legislation. Review the relevant declaration and supporting technical documentation.
Should every batch be independently tested?
Usually not. Type testing may establish a design’s capability, while routine factory tests, batch records, audits, and traceability provide production assurance. The needed frequency depends on the component, failure risk, contract, and applicable standards.
Can an old test report still be accepted?
Possibly, if the product design, materials, manufacturing controls, standard edition, and intended application remain covered. Age alone is not the only issue; applicability and current validity matter more.
Who should review the evidence?
The person accountable for the technical requirement should review it, with input from safety, quality, compliance, and installation specialists where the system is complex. Procurement should not be left to interpret technical limitations alone.
So, is it necessary to get independent testing for critical infrastructure safety components? When the component carries a serious consequence of failure, when performance cannot be verified after delivery, or when contractual and regulatory obligations demand objective evidence, the answer is usually yes. Match the test to the real duty, confirm that the supplied configuration is covered, and retain the records that show why the component was accepted.
Technical Specifications
- How to Select Electronic Hotel Key Card Locks for Guest Rooms and Staff AreasAuthor :Safety Compliance Lead
- How to Select Lab Instruments for Reliable Chemical Analysis WorkflowsAuthor :Precision Metrology Expert
- How to Size a UPS for Server Rooms: Load, Runtime, and Redundancy FactorsAuthor :Grid Infrastructure Analyst
Expert Insights

Chief Security Architect
Dr. Thorne specializes in the intersection of structural engineering and digital resilience. He has advised three G7 governments on industrial infrastructure security.
Related Analysis
- Sep 17, 2026How to Select Electronic Hotel Key Card Locks for Guest Rooms and Staff AreasAuthor :Safety Compliance Lead
- Sep 16, 2026How to Select Lab Instruments for Reliable Chemical Analysis WorkflowsAuthor :Precision Metrology Expert
- Sep 15, 2026How to Size a UPS for Server Rooms: Load, Runtime, and Redundancy FactorsAuthor :Grid Infrastructure Analyst
Core Sector // 01
Security & Safety
- What to Check When Sourcing Vibration Meters Wholesale for Industrial MaintenanceAuthor :Precision Metrology Expert

- How to Select Process Control Instruments for Accuracy, Safety, and UptimeAuthor :Precision Metrology Expert

- What Should Standards Compliance Analysis Training Cover Before an Audit?Author :Precision Metrology Expert

- Why Do Pressure Instruments Fail in High-Vibration Sites?Author :Precision Metrology Expert

- Is FM Software Integration Needed for Overseas Instrument Maintenance?Author :Precision Metrology Expert

- What Are the Differences Between Lab and Field Testing Equipment?Author :Precision Metrology Expert

- Is Independent Testing Necessary for Critical Safety Components?Author :Precision Metrology Expert

- How to Validate Industrial Application Scenarios Before ProcurementAuthor :Precision Metrology Expert