How to Select an Access Control Management System for Multi-Site Facilities
Author
Date Published
Reading Time
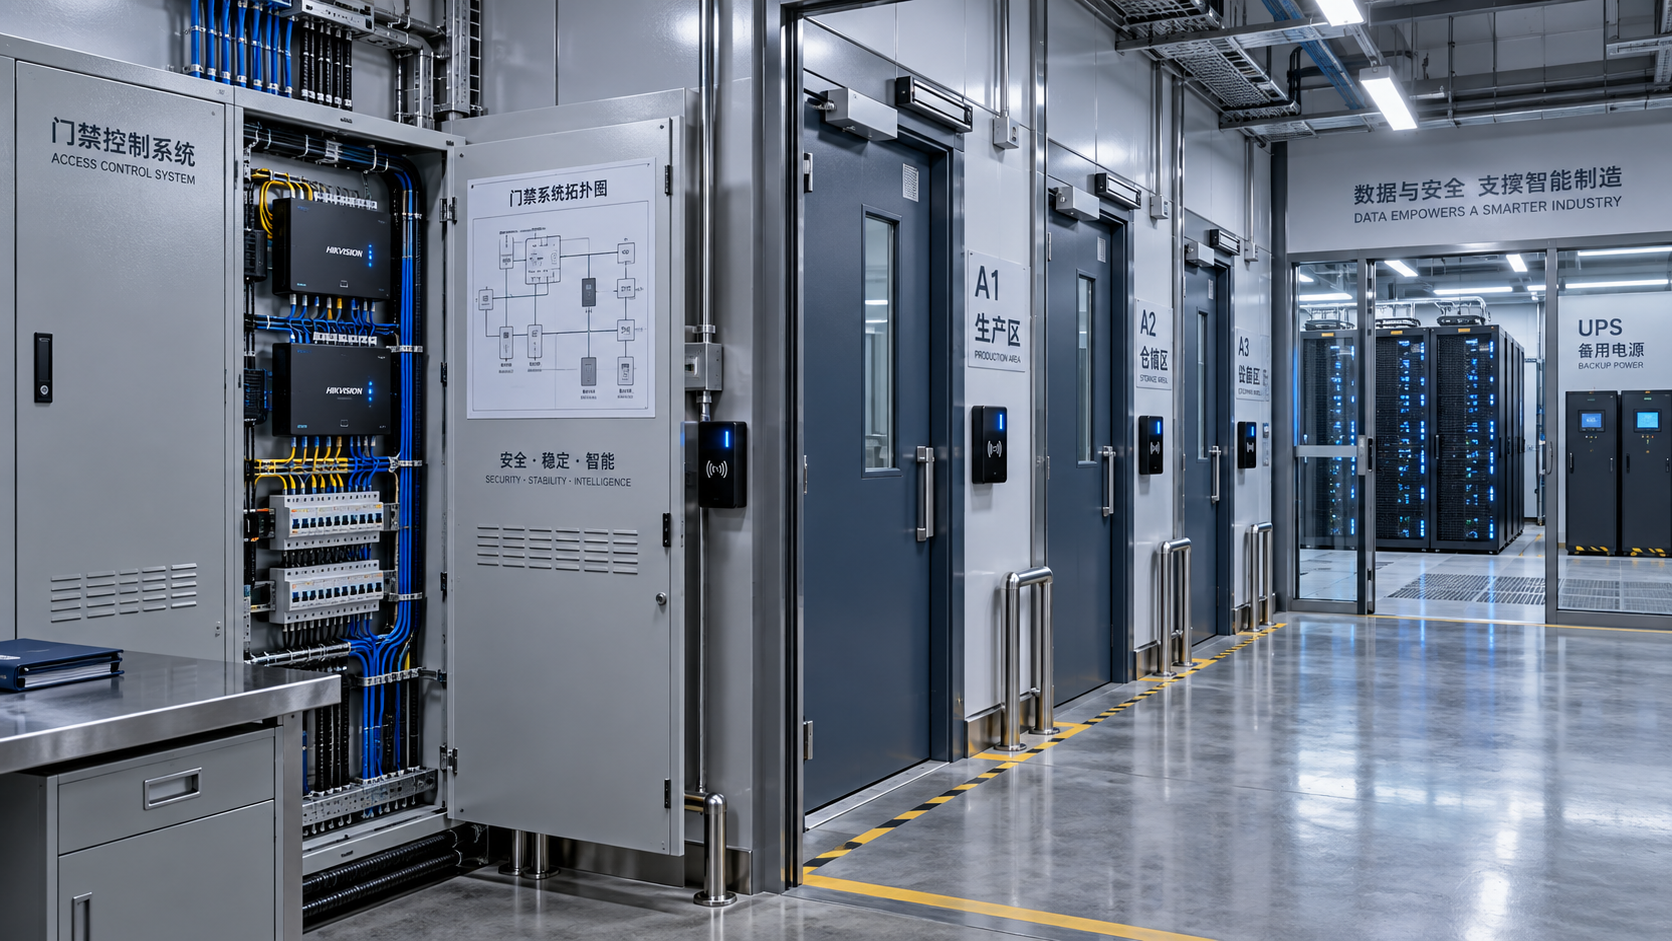
Selecting an access control management system for multiple facilities is primarily an architecture decision, not a reader or credential decision. The platform must apply a common identity and policy model across sites while preserving safe, reliable local operation when network links, cloud services, or central administration are unavailable. A system that performs well in a single building can become difficult to govern when facilities differ in age, connectivity, operational risk, regulatory obligations, and existing building systems.
The central question is not whether every door can be managed from one screen. It is whether the system can maintain trustworthy authorization decisions, auditable changes, and predictable recovery across the entire estate. That requires evaluating the control plane, field hardware, identity sources, integrations, cybersecurity model, and operating procedures as one system.
Start with the operating model, not the credential type
Multi-site access control has at least two layers of authority. The first is central governance: identity lifecycle management, role definitions, global access policies, reporting, audit retention, and administration. The second is site-level enforcement: controller decisions, local schedules, door behavior, alarm handling, and emergency operation.
These layers should be deliberately separated. A centrally hosted platform may simplify administration, but doors must not become unusable simply because a WAN connection fails. Controllers should retain the relevant cardholder permissions, schedules, door configurations, and anti-passback logic needed for local operation. The evaluator should establish what occurs during several distinct conditions:
- Loss of connectivity between a site and the central server or cloud tenant;
- Loss of connectivity between controllers and site management workstations;
- Controller restart, firmware failure, or database corruption;
- Expired certificates, unavailable identity services, or failed directory synchronization;
- Partial recovery, where communications return before all systems are fully synchronized.
“Offline capable” is not a sufficient answer. The relevant questions are how many credential records and event transactions are stored locally, which changes are queued, whether temporary access can be issued during an outage, how conflicts are resolved after reconnection, and whether the system produces a clear record of decisions made at the edge.
Operational differences between sites matter as much as technical topology. A distribution depot, laboratory, corporate office, remote utility station, and controlled manufacturing area may all need access control, but they do not require identical door states, approval paths, visitor rules, or emergency procedures. The platform should support common governance without forcing every site into an unsuitable uniform workflow.
Define what must be standardized and what must remain local
A frequent implementation error is attempting to standardize every configuration object. This produces a large global rule set that becomes harder to understand and easier to misapply. Conversely, allowing each site to define identities, roles, access groups, and naming conventions independently undermines the value of centralized management.
Useful global standards usually include identity attributes, unique personnel identifiers, credential issuance rules, role naming, access-review intervals, audit-event retention, administrator privileges, and interfaces to enterprise identity systems. Local configuration may reasonably include door names, opening schedules, muster points, local holiday calendars, alarm responses, and certain area-specific access groups.
The evaluation should therefore test whether the software can model hierarchy. A capable system can distinguish enterprise-wide policies from regional, site, building, and area-level rules, while showing which inherited rule grants a person access to a particular opening. Without this visibility, troubleshooting becomes slow: an operator may see that access was granted but not whether it resulted from a direct assignment, a role, an inherited group, a temporary exception, or an integration feed.
Role-based access control is valuable only when roles correspond to stable operational responsibilities. Using job titles alone often creates excessive exceptions because titles do not always describe location, shift pattern, contractor status, or risk authorization. A practical model commonly combines identity attributes with site assignment, work status, training or certification validity, and time-bound access conditions. The system should support this model without requiring custom scripts for routine policy changes.
Examine identity lifecycle and access governance
The most consequential access-control failure is often not a reader malfunction but a stale authorization. Multi-site facilities increase the risk because people move between locations, contractors rotate, temporary staff are onboarded rapidly, and identity data may originate in several systems.
An evaluation should map the full lifecycle: creation, identity proofing, credential issuance, activation, modification, suspension, expiration, lost-card response, replacement, and revocation. For each event, determine the authoritative source, the expected propagation path, the maximum acceptable delay, and the fallback procedure if synchronization fails.
Integration with HR, contractor management, directory, visitor, or learning-management systems should be assessed for data ownership rather than merely API availability. An API does not establish a reliable business process. For example, if an HR record marks an employee as terminated, the system must define whether physical access is removed immediately, at a scheduled interval, after a review, or through a separate security workflow. The answer may differ for voluntary departure, emergency suspension, and end-of-contract expiry.
Temporary access deserves particular scrutiny. A platform should allow expiration by date and time, controlled extensions, sponsor accountability, and reporting on credentials that remain active beyond the intended period. If the system uses broad “visitor” or “contractor” groups with manual removal, the administrative burden and exposure can grow rapidly across several sites.
Access reviews should be feasible at the level where accountability exists. A central security team may administer the platform, but local managers often need to confirm whether a person still requires entry to a plant, laboratory, data room, or restricted storage area. The system should produce reviewable lists that explain the access source and allow documented confirmation or removal. A generic report containing thousands of door permissions is not an effective governance control.
Evaluate controllers and field architecture as critical infrastructure
Management software is only one element of an access control management system. Door controllers, power supplies, input/output modules, locks, readers, enclosures, and communications networks determine whether the policy can be enforced under real operating conditions.
Controller capacity should not be evaluated only by the advertised number of doors. Confirm the maximum local cardholder database, transaction buffer, supported reader interfaces, encrypted communications options, firmware update method, and behavior under load. Multi-site designs can generate heavy event traffic during shift changes, evacuations, or widespread credential updates. The platform must preserve the integrity of authorization decisions even when event delivery to the central platform is delayed.
Reader-to-controller security is a significant distinction. Legacy reader interfaces may transmit credential data in forms that are easier to intercept or replay than modern supervised and encrypted interfaces. Where existing infrastructure must remain in service, the assessment should identify which portions of the estate retain legacy exposure and whether compensating controls are available. Replacing a card technology while leaving insecure reader wiring or permissive controller configuration unchanged may deliver less improvement than expected.
Door hardware must also align with the security objective and life-safety requirements. Fail-safe and fail-secure locking behavior cannot be chosen solely for security preference; it must be coordinated with fire alarm interfaces, means-of-egress requirements, local codes, and the function of the opening. Access control software can command a door, but it cannot correct an inappropriate lock selection, inadequate power design, or poorly supervised emergency release circuit.
For industrial or remote facilities, environmental suitability is equally material. Controller and enclosure selection should consider temperature, humidity, dust, vibration, electrical noise, surge exposure, and backup power duration. A centralized platform does not compensate for field devices that cannot operate reliably in local conditions.
Interoperability should be proven at workflow level
Multi-site programs commonly involve a mixture of new and inherited systems: video management, intrusion detection, visitor management, elevator control, intercom, identity directories, building management platforms, and incident-management tools. The relevant question is not whether a vendor lists an integration. It is whether the integration supports the workflow required at the required scale.
For video integration, clarify whether an access event can retrieve associated video, whether timestamps are synchronized, whether operators can acknowledge alarms across systems, and whether video retention and permissions remain governed by the video platform. For elevators, confirm how floor permissions are assigned, what happens during controller or network loss, and whether emergency operation overrides access rules correctly.
Open interfaces can reduce dependency on a single supplier, but “open” should be examined closely. Documented APIs, supported software development kits, standard reader protocols, exportable event data, and independent controller compatibility are different claims. A system may expose an API while still requiring proprietary middleware or limiting essential functions to vendor-specific hardware.
Compatibility testing should include existing credential populations. Card formats, mobile credentials, PIN use, biometric templates where permitted, and credential enrollment equipment can introduce migration constraints. If a phased replacement is planned, determine whether old and new readers can coexist, whether credentials work consistently across both environments, and how duplicate identities are prevented during transition.
Cybersecurity is a selection criterion, not an add-on
Access control connects identity data with physical entry points. A compromise can affect confidentiality, operational continuity, and physical security simultaneously. The system should therefore be assessed using the same discipline applied to other operational and enterprise systems.
Key controls include strong administrator authentication, role separation, least-privilege access, encrypted communications, certificate management, secure credential storage, signed firmware, controlled remote support, event logging, vulnerability disclosure practices, and a defined patching process. The evaluation should identify which components are cloud-managed, which remain on premises, where data is stored, and how remote connectivity is established.
Administrative roles need special attention in a distributed estate. A regional operator may require the ability to manage local badges and alarms but should not necessarily be able to alter global role definitions, export all personnel data, or change cybersecurity settings. The system should provide granular permissions and reliable logs of configuration changes, not only door events.
Ask how the supplier handles end-of-support hardware and software. Long-lived physical security systems are often retained beyond their original IT assumptions. A credible lifecycle plan states supported versions, firmware maintenance expectations, vulnerability response channels, backup and restore procedures, and the process for replacing obsolete components without losing historical records or access-policy integrity.
Compliance must be translated into system behavior
Compliance requirements vary by jurisdiction, facility type, and the personal data processed. Standards and certifications associated with devices, electrical equipment, fire interfaces, or cybersecurity can be relevant, but they do not automatically prove that the deployed system meets local obligations.
For personal data, determine what information is stored in credentials, access logs, visitor records, and biometric systems; who can view it; where it is hosted; how long it is retained; and how deletion or export requests are handled where applicable. Biometric access should be approached with particular care because legal restrictions, consent requirements, and acceptable use conditions differ significantly across jurisdictions.
Auditability is often more important than a compliance label. The platform should preserve an intelligible record of who changed a permission, when it changed, what approval supported it, and what access was effective at a given time. If investigations require correlating events across sites, clocks on controllers, servers, video systems, and identity platforms must be synchronized through a controlled time source.
Test scalability through realistic failure and change scenarios
Scalability is not simply the maximum number of doors stated in a specification. It includes the ability to onboard a new site, import identities, apply templates, manage different time zones and holiday calendars, upgrade firmware, search events, and recover from faults without creating administrative inconsistency.
Before selection, use representative scenarios in a proof of concept or structured technical demonstration. These should include a central policy change affecting several sites, a local network outage, revocation of a contractor credential, controller replacement, bulk personnel import, alarm handling during high event volume, and restoration from backup. The purpose is to observe operational behavior, not merely confirm that a feature exists in a product presentation.
Configuration portability is especially important for expansion. Site templates can accelerate deployment, but they must be versioned and controlled. Otherwise, copying a previous site configuration may also copy obsolete access groups, inappropriate schedules, or local exceptions that do not apply to the new location.
Choose for recoverability and evidence, not dashboard appearance
A polished centralized dashboard can conceal weak operational controls. The stronger selection is the platform that makes authorization sources visible, continues secure local operation during central-service disruption, integrates through documented and supportable interfaces, and provides evidence for every material change.
Access control management systems for multi-site facilities should be judged by how they behave when personnel records change, networks fail, hardware is replaced, a site is acquired, or an investigation requires reconstructing access decisions. Those conditions reveal whether centralized management is delivering genuine control or merely centralizing administration.
Technical Specifications
- How to Select an Access Control Management System for Multi-Site FacilitiesAuthor :Safety Compliance Lead
- Portable Gas Monitor Calibration: How Often Is It Needed for Safe Confined-Space Work?Author :Precision Metrology Expert
- Wholesale Borosilicate Lab Glassware: How Buyers Verify Quality, Specs, and Supply ReliabilityAuthor :Precision Metrology Expert
Expert Insights

Chief Security Architect
Dr. Thorne specializes in the intersection of structural engineering and digital resilience. He has advised three G7 governments on industrial infrastructure security.
Related Analysis
- Sep 20, 2026How to Select an Access Control Management System for Multi-Site FacilitiesAuthor :Safety Compliance Lead
- Sep 19, 2026Portable Gas Monitor Calibration: How Often Is It Needed for Safe Confined-Space Work?Author :Precision Metrology Expert
- Sep 18, 2026Wholesale Borosilicate Lab Glassware: How Buyers Verify Quality, Specs, and Supply ReliabilityAuthor :Precision Metrology Expert
Core Sector // 01
Security & Safety
- How to Select an Access Control Management System for Multi-Site FacilitiesAuthor :Safety Compliance Lead

- How to Select Electronic Hotel Key Card Locks for Guest Rooms and Staff AreasAuthor :Safety Compliance Lead

- How to Evaluate a Hotel Key Card Lock Supplier for Multi-Property RolloutsAuthor :Safety Compliance Lead

- Pre-Contract Audit Checklist for Verified Production Safety and Environmental ComplianceAuthor :Safety Compliance Lead

- How Can Distributors Build Procurement-Oriented Industrial Content That Drives RFQs?Author :Safety Compliance Lead

- EU Mandates EN 50131-1:2026 for Security SystemsAuthor :Safety Compliance Lead

- EU EN 50131-1:2026 Takes Effect on CCTV ComplianceAuthor :Safety Compliance Lead

- IEC Issues CCTV Interoperability Test StandardAuthor :Safety Compliance Lead